Daily brief · October 23, 2026

AI enters the hot path—and resilience becomes policy.

Bounded AI decisions, machine-speed attacks, exposed platform secrets, explicit Copilot defaults, regional secret monitoring and unified Kubernetes operations define the day.

14 minute read6 developmentsPrimary sources first
01
AI & Models5 min read

OpenAI makes the Decisions API generally available

OpenAI made its GPT-6 Luna-powered Decisions API generally available for bounded decisions from text, images and native JSON. It returns a probability, one predefined choice or a rubric score; supports as many as 400 questions per request; adds prompt caching, US and EU inference residency and native GPT-Live integration; and is priced only on input tokens. OpenAI says it can be up to ten times faster than Luna through the Responses API.

Why it mattersLow-latency classification and routing can now sit directly in application and agent hot paths, but a bounded answer is still probabilistic. Teams should calibrate thresholds on representative data, define abstain or human-review paths, version questions and rubrics, and trace every downstream action that a decision authorizes.

Source: OpenAI ↗ · Published October 22, 2026

#Decisions API#GPT-6 Luna#real-time AI#structured outputs
02
Security5 min read

Railway tells users to rotate every stored environment variable

Railway said an unauthorized third party may have accessed encrypted customer environment variables and obtained decrypted contents for some of them. The company warned that those variables can contain API keys and database or registry credentials, paused deployments during its investigation and advised every user to rotate all environment variables and review downstream service logs.

Why it mattersA platform secret can become access to many other systems even when the application itself was not breached. Teams should revoke and reissue credentials rather than only editing values, start with high-privilege and production keys, invalidate active sessions where possible, and use provider logs to determine what the exposed credentials reached.

Source: Railway Security Disclosure ↗ · Published October 21, 2026

#Railway#secrets#credential rotation#incident response
03
Security6 min read

Microsoft attributes the ConnectWise campaign to an agentic attack framework

Microsoft assessed that China state-aligned Storm-0940 used the open-source ARTEX multi-agent penetration-testing framework to automate attacks against hundreds of organizations and was responsible for the ConnectWise multi-tenant application compromise. Microsoft observed reconnaissance, password spraying and OAuth application abuse; in several ARTEX-driven cases, the actor obtained privileged cloud access in under three hours.

Why it mattersAgentic offense compresses the interval between first signal and privileged persistence. Defenders should preserve evidence before removing applications, inventory affected service principals by application ID, correlate app-only sign-ins with Graph and directory changes, rotate credentials, revoke excess grants and make high-risk app-role changes interruptible in minutes rather than business hours.
Read the updated cyber-AI governance guide

Source: Microsoft Security Blog ↗ · Published October 21, 2026

#ARTEX#Storm-0940#ConnectWise#OAuth security
04
AI Coding4 min read

GitHub begins enforcing a global default for Copilot features

GitHub began a gradual October 22–26 rollout that applies an enterprise or organization’s selected global default to eligible generally available Copilot features and MCP-server settings still marked Unconfigured. Explicit per-feature choices are preserved, previews remain opt-in and the default is applied once rather than continuously rewriting policies.

Why it mattersAn unconfigured control can now become an effective allow or deny decision. Copilot administrators should review the global default before rollout, export current exceptions, assign ownership for new-feature review and explicitly set sensitive features so future availability changes do not become accidental production policy.

Source: GitHub Changelog ↗ · Published October 22, 2026

#GitHub Copilot#MCP#enterprise policy#AI governance
05
Security4 min read

GitHub extends public secret monitoring to data-residency enterprises

GitHub put public monitoring into public preview for Enterprise Cloud customers with data residency. Secret scanning can now monitor public commits across GitHub and attribute exposed credentials to an enterprise using verified email-domain matching; alerts are encrypted and delivered to the enterprise dashboard in its designated region without sharing the regional membership roster with github.com.

Why it mattersCredentials can leak outside repositories the enterprise owns, but regional isolation changes how attribution works. Security teams should verify every corporate domain, establish alert ownership and revocation targets, test false-attribution handling, and treat public monitoring as an additional detection layer rather than a substitute for push protection and short-lived credentials.

Source: GitHub Changelog ↗ · Published October 22, 2026

#secret scanning#data residency#GitHub Enterprise#credential exposure
06
Cloud & Infrastructure5 min read

Nutanix unifies virtualized and bare-metal Kubernetes in NKP 2.19

Nutanix made Kubernetes Platform 2.19 generally available with one declarative operating model for virtualized and bare-metal clusters. NKP Metal adds automated node discovery, Ubuntu imaging and cluster provisioning; the release also adds multi-writer AOS storage, UI-driven upgrade checks, a VM Operator path, an AI catalog and validated AMD Instinct MI350 support subject to documented prerequisites.

Why it mattersA shared control plane can reduce separate operational silos for virtualized, bare-metal and AI workloads, but it also concentrates upgrade and policy risk. Platform teams should validate hardware prerequisites, failure domains, CSI semantics, rollback behavior and whether the promised common workflow preserves workload-specific isolation and performance.

Source: Nutanix Blog ↗ · Published October 22, 2026

#Nutanix NKP#Kubernetes#bare metal#AI infrastructure

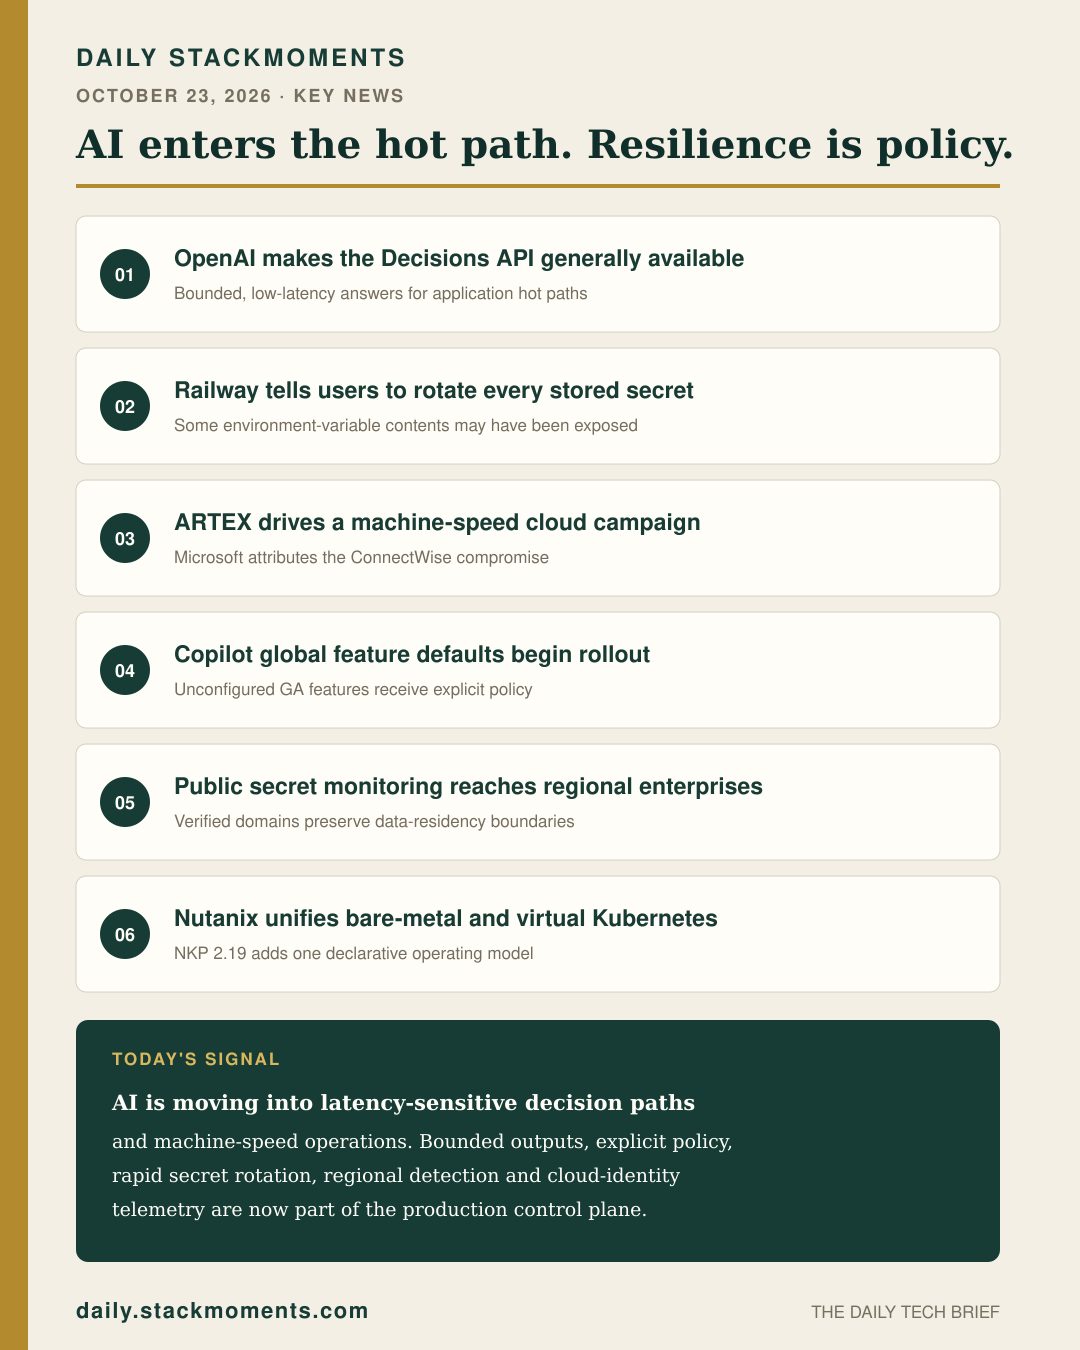
Shareable visual

Poster of the Day

Today's six verified developments and technology signal, ready to share.

Daily StackMoments 1080 by 1350 poster summarizing six key technology developments for October 23, 2026Download poster ↓