01
Security5 min read
Google warns cloud users to remove compromised CA trust
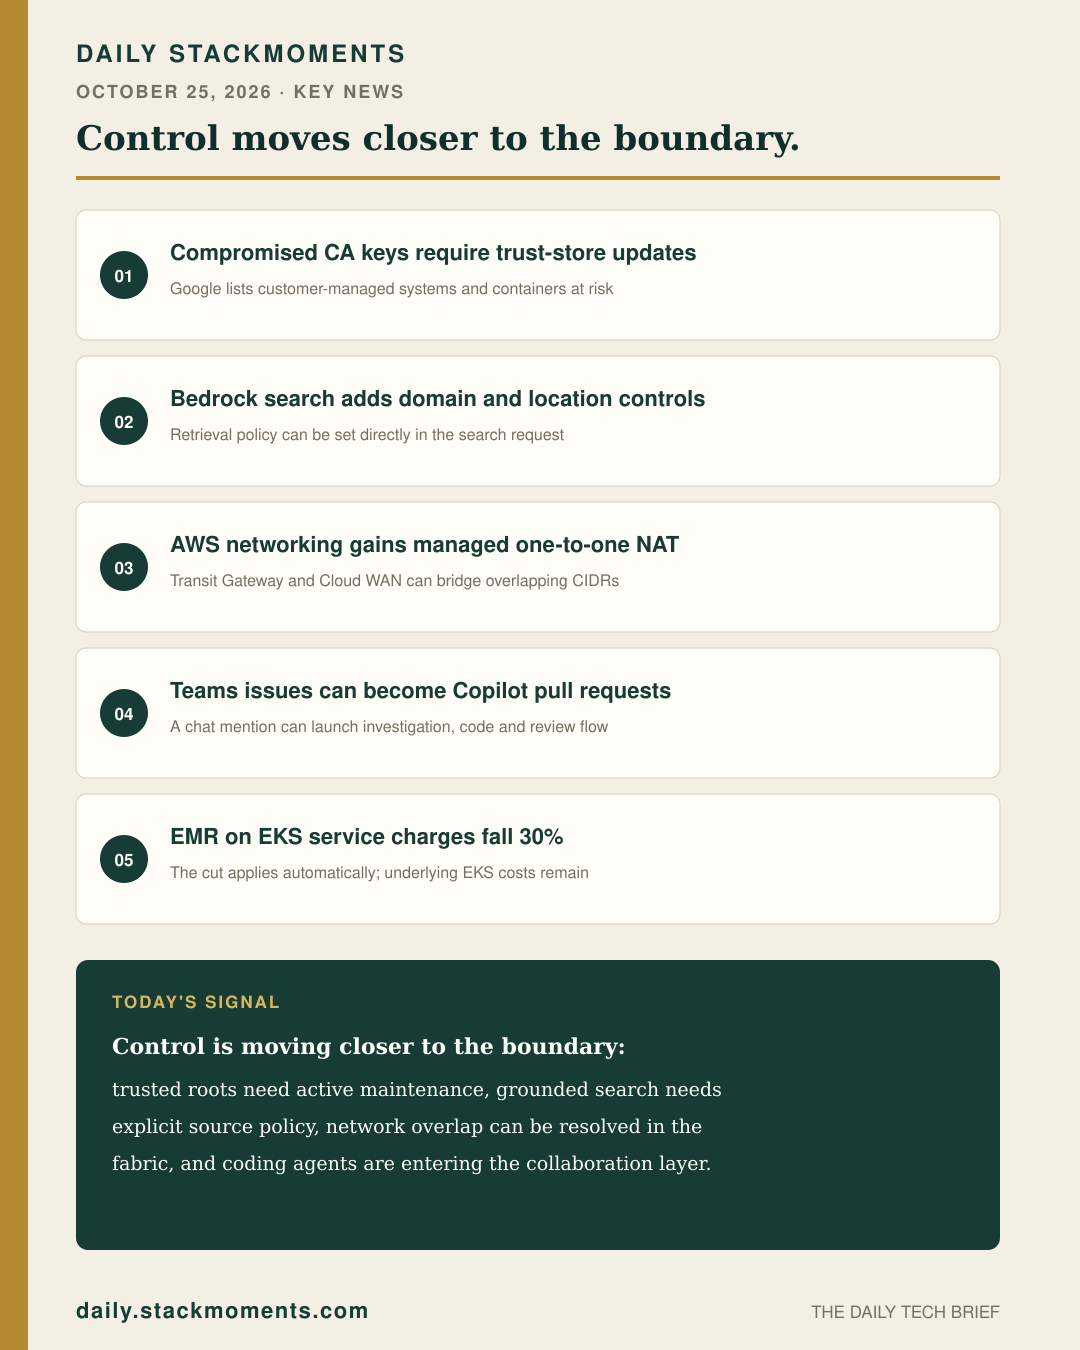
Google Cloud disclosed that weak cryptographic randomness exposed private keys for eight eMudhra subordinate certificate authorities, including certificates cross-signed by AAA Certificate Services. Google said its infrastructure was not breached and it saw no exploitation against Google Cloud workloads, but customer-managed operating systems, custom container images and bundled trust stores may still trust the affected roots across services including GKE, Compute Engine, Cloud Run, Vertex AI and managed databases.
Why it mattersA compromised subordinate CA can enable forged TLS certificates and interception even when application code is unchanged. Platform teams should update OS and container trust stores, refresh the Google Cloud CLI, restart or upgrade affected COS nodes, rebuild base images and verify service-specific patch guidance rather than assuming managed-cloud mitigation covers customer-owned dependencies.
Source: Google Cloud Security Bulletin GCP-2026-071 ↗ · Published October 23, 2026
#PKI#certificate authorities#GKE#TLS
02
AI & Models4 min read
Bedrock Web Search adds domain and location controls
AWS added allowed-domain and blocked-domain filters plus optional user-location parameters to the Web Search tool in Amazon Bedrock. Developers can set as many as 100 allowed or blocked domains in an existing OpenAI Responses API request, while location data can make search results more geographically relevant. The controls are available in the four AWS Regions where Bedrock Web Search is supported.
Why it mattersGrounding policy can now be expressed in the retrieval request instead of enforced only after results return. Teams should maintain reviewed domain sets, log the effective policy, minimize location precision, evaluate regional bias and still validate citations because a permitted source is not automatically accurate or current.
Source: AWS What's New ↗ · Published October 23, 2026
#Amazon Bedrock#web search#grounding#Responses API
03
Cloud & Infrastructure5 min read
AWS brings managed 1:1 NAT to Transit Gateway and Cloud WAN
AWS added one-to-one network address translation directly to Transit Gateway and Cloud WAN attachments through Regional Private NAT Gateway. The capability translates overlapping private CIDR ranges bidirectionally across VPC, Site-to-Site VPN, Direct Connect and SD-WAN connections without a customer-operated NAT appliance or separate return-traffic rules, with CloudWatch metrics and EventBridge events for translated traffic.
Why it mattersOverlapping address space is a recurring blocker in acquisitions, partner connectivity and multicloud integration. Network teams can remove bespoke appliances, but should model translation ranges centrally, test asymmetric paths and DNS behavior, monitor exhaustion and preserve an auditable mapping from translated addresses to original workloads.
Source: AWS What's New ↗ · Published October 23, 2026
#AWS Transit Gateway#Cloud WAN#NAT#networking
04
AI Coding4 min read
GitHub turns Teams issue notifications into Copilot pull requests
GitHub consolidated notifications and Copilot in its updated Microsoft Teams app. From a channel, group chat or private chat, a developer can mention GitHub on an issue notification and ask Copilot to investigate, implement a fix and open a pull request. GitHub said the legacy Teams app will be renamed deprecated and retired on November 16, while existing notification installations can update to the consolidated app.
Why it mattersThe collaboration surface is becoming an execution surface. Engineering leaders should restrict repository selection, require branch protection and review, preserve the originating conversation as context, audit app permissions and avoid treating a chat mention as sufficient authorization for sensitive code changes.
Source: GitHub Changelog ↗ · Published October 23, 2026
#GitHub Copilot#Microsoft Teams#coding agents#pull requests
05
Cloud & Infrastructure4 min read
AWS cuts the EMR-on-EKS service charge by 30%
AWS reduced the EMR service charge added to EKS by 30% for both per-vCPU-hour and per-GB-hour dimensions. The automatic reduction applies to all EMR-on-EKS workloads in every supported Region; underlying EKS and other infrastructure charges are unchanged.
Why it mattersA lower orchestration surcharge changes the break-even point for teams running Spark on shared Kubernetes. FinOps and data-platform teams should rerun workload-level cost comparisons with EC2, storage, network and EKS charges included, then validate whether cluster utilization and operational overhead still favor EMR on EKS over alternatives.
Source: AWS What's New ↗ · Published October 23, 2026
#Amazon EMR#Amazon EKS#Apache Spark#FinOps